Access logs, config snapshots, and audit trails pulled automatically from the systems that generate them, instead of someone screenshotting a settings page every quarter for an auditor. We build the automation; your compliance program stays with your counsel or GRC platform.
Compliance evidence, collected once instead of chased quarterly
The problem, reframed
A SOC 2 or GDPR audit does not fail because a company is doing something wrong, it usually fails on time because evidence collection is still manual: someone logging into six different systems to screenshot access lists, export config settings, and compile a spreadsheet nobody wants to maintain every quarter. Platforms like Vanta, Drata, and Secureframe solve the framework and dashboard side of this well. They still need real engineering to pull evidence from your actual internal systems, the ones outside their native integration list, into that dashboard automatically.
We are not auditors and we do not certify anyone's compliance posture. What we build is the pipeline that gets accurate evidence into your compliance platform, or your own audit store, on a schedule, so the humans doing the actual audit work are reviewing current data instead of assembling it by hand first.
What we build
01
Evidence collection pipelines.
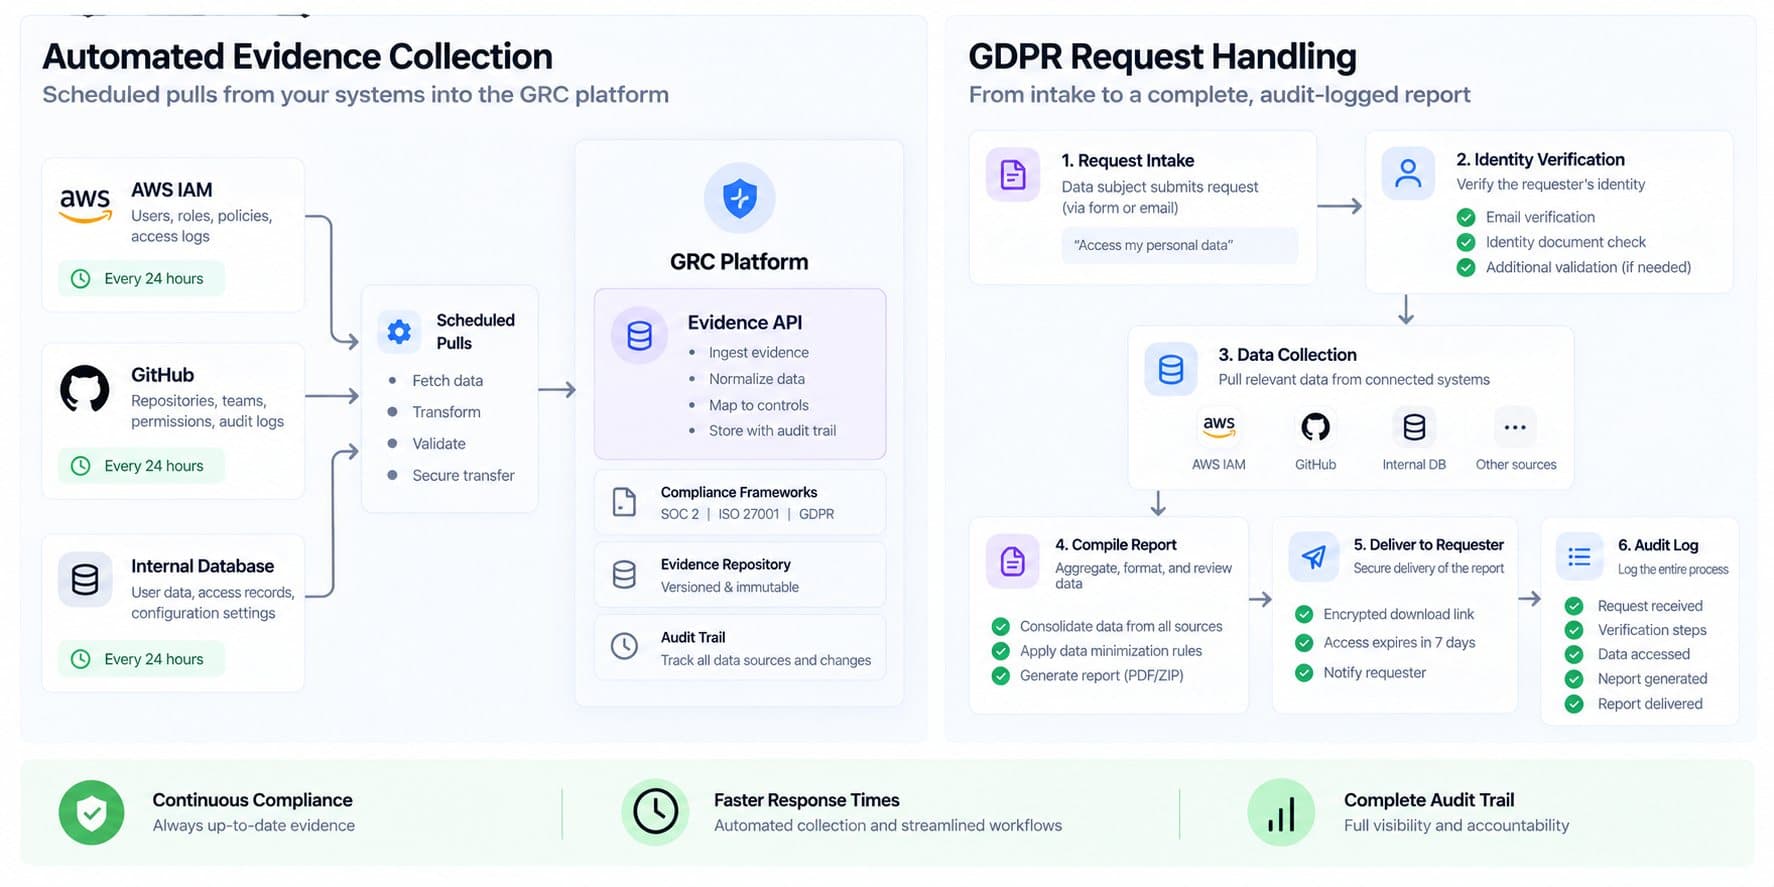
Scheduled pulls of access logs, IAM configuration, deployment records, and infrastructure settings from AWS, GCP, Azure, and GitHub, written directly into your GRC platform's API or into your own audit trail store if you are not on one of the major platforms. Built around your actual system inventory, not a generic checklist that assumes every company runs the same stack.
02
GDPR and CCPA data subject request automation.
An intake flow with identity verification, an automated search across your CRM, database, and email systems for the requester's data, and a compiled report or deletion workflow with a full audit trail of what was searched, found, and actioned. The legal determination of what counts as a valid request stays a human decision; the search and compilation work is where automation actually removes the manual burden.
03
Centralized, queryable audit logging.
Logs from disparate systems consolidated into one Postgres-backed store with retention policies enforced automatically rather than depending on someone remembering to archive or purge on schedule. Where tamper-evidence matters, we build append-only logging patterns rather than a table anyone with database access could quietly edit.
04
Access review automation.
A recurring workflow that pulls current user and role lists from your systems, routes them to the right approver, logs the sign-off with a timestamp, and flags accounts that look stale or orphaned, replacing a quarterly spreadsheet exercise with a process that runs itself and leaves a clean trail.
05
Policy-as-code checks where they are viable.
Automated checks against infrastructure configuration, encryption at rest enabled, MFA enforced on privileged accounts, run continuously instead of during a manual quarterly review, flagging drift the moment it happens rather than the moment someone next remembers to look.
Recently shipped
Built for a SaaS company preparing for their first SOC 2 audit. We built scheduled evidence collection pipelines pulling access logs from AWS IAM, deployment records from GitHub, and configuration snapshots from their internal admin system, writing structured evidence into their Vanta dashboard automatically. A quarterly access review workflow pulled current user lists, routed them to the right approver, and logged every sign-off with a timestamp. The team stopped screenshotting settings pages and started reviewing current evidence instead of assembling it by hand.
Built on a modern, connected stack
Self-hosted n8n orchestrates the scheduled evidence pulls and the request-handling workflows, Postgres holds the centralized audit trail, and where your existing CRM or helpdesk; HubSpot, Zoho, Salesforce, Zendesk, Freshdesk, or Intercom; holds customer data relevant to a GDPR request, the automation reads directly from those systems instead of asking someone to search them by hand. If the pipeline needs a real tool layer between the workflow and your infrastructure APIs, an MCP server we build slots directly into the same architecture.
Who this is for
01
Startups and SaaS companies going through SOC 2 for the first time,
where evidence collection is eating engineering time that should be going into the actual product.
02
Companies with GDPR or CCPA obligations
still fulfilling data subject requests manually, one email and one spreadsheet search at a time.
03
Teams already on Vanta, Drata, or Secureframe
who have hit the gap where a custom or internal system isn't natively supported and evidence for it still gets collected by hand.
04
Ops or security teams
running access reviews on a spreadsheet that nobody enjoys maintaining and that produces no real audit trail of who approved what.
Why Flowagenz
Automation code you own outright.
Full ownership of every workflow and pipeline built for you. Nothing depends on a Flowagenz-run system to keep evidence flowing into your compliance platform.
Based in Salem, Tamil Nadu.
Western-grade engineering at a rate structure offshore delivery makes possible.
Real overlap, not vague promises.
Async-first communication with working hours that overlap US Eastern mornings, UK afternoons, and Australian business hours on the same day.
We stay in our lane on purpose.
We build the automation that makes evidence collection, request handling, and access reviews reliable and auditable. We are not your auditor, your lawyer, or a substitute for your GRC platform's compliance guidance, and we will say so plainly rather than implying a piece of automation makes you compliant by itself.
How it works
01
01
System inventory and scoping call.
We map which systems generate the evidence your framework actually requires, and confirm whether you are automating into an existing GRC platform or building your own audit store.
02
02
Pipeline design.
Evidence collection schedules, request-handling flows, and access review cadences designed around your real systems and your framework's actual evidence requirements.
03
03
Build and testing.
Pipelines built and tested against your real systems, including a dry run of the GDPR or CCPA request flow before it ever processes a live request.
04
04
Handover and monitoring setup.
Documentation for your team, plus alerting if a scheduled evidence pull fails so a gap gets caught immediately instead of surfacing during the next audit. Typical builds run 3 to 6 weeks depending on system count and framework scope.
What you get on handover
Every AI compliance automation build ships with the following:
Full source code for every evidence collection pipeline, request-handling workflow, and access review automation
Evidence collection pipelines pulling from your actual systems on a defined schedule, writing into your GRC platform or audit store
GDPR or CCPA request-handling flow with identity verification, data search, and compiled report or deletion workflow with full audit trail
Centralized audit logging in Postgres with retention policies and append-only patterns where tamper-evidence matters
Access review automation pulling current user lists, routing to approvers, logging sign-offs with timestamps
Policy-as-code checks running continuously against infrastructure configuration with drift alerting
System inventory documentation mapping every evidence source to its framework requirement
Runbook and troubleshooting guide for your team to extend, monitor, and maintain every pipeline
Alerting configuration for failed evidence pulls, stale access reviews, or policy drift
API key and environment variable list with secure storage guidance
Staging and production testing notes documenting what was validated against your real systems
30-day post-launch support for pipeline tuning, alert threshold adjustment, and integration refinements
Zero dependency on Flowagenz infrastructure; everything lives in your n8n, your database, your control
FAQ
Frequently Asked Questions
Everything you need to know about our process and digital systems.
No, and we will not claim it does. Compliance is a program your team runs, informed by your auditor and legal counsel. What we build makes the evidence collection and operational workflows underneath that program faster and more reliable, which is a real and meaningful piece of it, but it is not a substitute for the program itself.
Stop collecting evidence by hand every quarter
Tell us which framework you are working toward and which systems are the most painful to pull evidence from manually, and we will scope the automation on a short call. No generic pitch.